Cybersecurity Risk Assessment Checklist

An Actionable Cybersecurity Risk Assessment Checklist and Guide
Most organisations discover their security gaps after a breach, which is the expensive way. The average cost of a data breach reached $4.88 million in 2024, making the financial consequences of security failures impossible to ignore. Yet the single most effective tool for preventing that scenario, a structured cybersecurity risk assessment, remains either poorly executed or skipped entirely at many companies.
This article walks you through a practical, step-by-step process for conducting one, provides a downloadable checklist you can customise for your organisation, and compares the major frameworks so you can pick the right fit.
Why a risk assessment is your first line of defense
A cybersecurity risk assessment tells you what threats you face, their potential impact, how likely they are, and what they would cost your business.
Without that information, security spending becomes reactive, with budgets allocated based on vendor pitches, headline attack types, or the loudest voice in the room rather than actual exposure. By the time a security incident reveals a gap, the damage may already be done. A proper risk assessment helps organisations identify and address weaknesses before they are exploited, rather than closing the stable door after the horse has bolted.
The strategic value goes beyond defense. A well-documented risk assessment gives you concrete data to bring into budget conversations with the board. Instead of arguing that better endpoint protection is needed, for example, you can show that the probability of a ransomware event affecting your ERP system carries an estimated annual loss exposure of £1.84m, and that a £144k investment in specific controls reduces that exposure by 70%. That is a conversation executives can act on.
Risk assessments also highlight the friction points between legacy systems and new digital initiatives. If you are migrating workloads to the cloud or integrating a newly acquired company’s infrastructure, the assessment process forces you to map dependencies, identify trust boundaries, and document assumptions that would otherwise remain invisible until something breaks.
The core components of a cybersecurity risk assessment
Every risk assessment rests on three pillars, and confusing them leads to wasted effort.
- Threats are the actors and events that could cause harm, such as ransomware gangs, phishing campaigns, disgruntled employees, and natural disasters affecting data centers. These exist independent of your organisation, so you can assess their likelihood, but you cannot control them.
- Vulnerabilities are the weaknesses in your systems, processes, or people that a threat could exploit, like unpatched software, overly permissive access controls, lack of multi-factor authentication, or a development team deploying containers without scanning images. These are factors that you do control.
- Impact is what happens to your business when a specific threat exploits a specific vulnerability. It can include revenue loss, regulatory fines, reputational damage, operational downtime, and intellectual property theft.
Think of a threat as a burglar in your neighborhood. A vulnerability is an unlocked window, and impact is what you lose when they climb through it. Risk sits at the intersection of all three.
The mistake most teams make is treating these as abstract categories on a spreadsheet. They list malware as a threat, weak passwords as a vulnerability, and data loss as an impact, then assign a color code. That exercise produces a heat map that looks impressive in a slide deck but tells you almost nothing about where to spend your next investment. The goal is to be specific about which systems, which threat actors, which business processes, and how much money.
A step-by-step guide to conducting your cybersecurity assessment
The seven steps below follow the risk assessment process most organisations use in practice. They also map directly onto ISO/IEC 27001:2022, which sets out its requirements in clauses 4 to 10 and its reference controls in Annex A. If certification is on your roadmap, working through these steps produces most of the documented evidence an auditor will ask for.
Step 1
Identify your risk appetite
Before assessing individual risks, agree on how much risk your organisation is prepared to accept. Your risk appetite provides the benchmark for deciding which risks require action, which can be monitored, and which may be accepted as part of doing business.
This should be agreed at an organisational level and reflect factors such as regulatory obligations, business objectives, financial exposure, and the potential impact on customers and operations. Without a clear risk appetite, risk assessments can identify a long list of risks without providing a clear basis for deciding what needs to change.
In ISO 27001 terms: clause 6.1.2 requires you to define your information security risk criteria, including risk acceptance criteria, before you assess anything. Clause 5.1 puts responsibility for this with top management. An appetite statement that has not been signed off at leadership level will not satisfy either.
Step 2
Define the scope
Start by identifying what you are assessing. Set boundaries, such as a specific business unit, product line, cloud environment, or regulatory domain like systems handling personal data under UK GDPR.
Within that scope, catalogue your important assets, from customer databases and source code repositories to payment processing systems, third-party integrations, and employee personal data. Then assign ownership. If nobody owns an asset, it is already a vulnerability.
In ISO 27001 terms: clause 4.3 requires a documented ISMS scope, informed by the context and interested parties you identify under clauses 4.1 and 4.2. The asset catalogue and its named owners satisfy Annex A control A.5.9, inventory of information and other associated assets. Exclusions matter as much as inclusions: an undocumented exclusion becomes an unmanaged risk, and an unjustified one is an audit finding.
Step 3
Identify threats and vulnerabilities
Use multiple inputs. Internal sources include past incident reports, security-related help desk tickets, and results from previous penetration tests. External sources include threat intelligence feeds, industry-specific threat reports (financial services face different primary threats than healthcare), and vulnerability databases like the NIST National Vulnerability Database.
Do not limit this to technical or physical threats, as business email compromise, social engineering, and supply chain attacks consistently cause more damage than exotic zero-day exploits. Brainstorming sessions with cross-functional teams (engineering, operations, legal, HR) surface risks that a purely technical review will miss.
In ISO 27001 terms: clause 6.1.2 c) requires you to identify the risks to confidentiality, integrity and availability within your scope, and to identify a risk owner for each one. The inputs described above are themselves Annex A controls: A.5.7 threat intelligence, A.8.8 management of technical vulnerabilities, and A.5.27 learning from information security incidents.
Step 4
Analyse likelihood and impact
For each threat-vulnerability pair, assess how likely exploitation is and how severe the consequences would be.
You can do this qualitatively (High/Medium/Low scales) or quantitatively (probability percentages and financial amounts). For most organisations, starting with a qualitative assessment and then applying quantitative methods to the top-tier risks is the most practical approach.
In ISO 27001 terms: clause 6.1.2 d) requires you to assess consequences and likelihood and determine a level of risk for each one. Clause 6.1.2 e) then requires you to compare those levels against the acceptance criteria you set in step 1 and prioritise accordingly. The standard does not mandate a particular scale, but it does require that the method produces consistent, comparable and repeatable results. In practice that means writing down what a “4” means for likelihood and impact before anyone starts scoring, not after.
Step 5
Evaluate existing controls
Document what is already in place, such as firewalls, intrusion detection systems, encryption at rest and in transit, access management policies, and incident response plans. Then assess whether those controls actually work. A firewall rule that has not been updated in two years may be worse than no firewall at all because it creates a false sense of security.
In ISO 27001 terms: this is what separates inherent risk from residual risk, and residual risk is the number clause 6.1.3 asks your risk owners to approve. Be honest about effectiveness. A control that exists on paper, covers part of the estate, or has never been tested is partial, not implemented, and scoring it otherwise produces an assessment that flatters you into inaction.
Step 6
Prioritise and treat risks
With your analysed list, you have four options for each risk:
- Mitigate it (implement or improve controls)
- Transfer it (insurance or contractual allocation)
- Accept it (the cost of mitigation exceeds the expected loss)
- Avoid it (stop the activity creating the risk)
The output should be a risk register with clear owners, deadlines, and defined actions.
In ISO 27001 terms: clause 6.1.3 covers risk treatment and adds three requirements that organisations routinely miss. First, compare the controls you have chosen against Annex A to confirm you have not overlooked anything — all 93 controls must be considered, not implemented. Second, produce a Statement of Applicability recording which Annex A controls apply, their implementation status, and a written justification for any exclusion. Undocumented exclusions are one of the most common Stage 2 audit findings. Third, obtain risk owners’ approval of the treatment plan and formal acceptance of the residual risks. An accepted risk with no named person behind it is not an accepted risk.
Step 7
Monitor, review and improve
A risk assessment is a snapshot. Threats change, systems change, and controls decay. Set a review cycle — annually as a minimum — and reassess whenever something material changes: a new system, a significant supplier, an incident, a restructure, or a change in regulatory obligations.
In ISO 27001 terms: clause 9.1 requires you to monitor and measure whether controls are working, clause 9.2 requires internal audit, and clause 9.3 requires management review at planned intervals. Clause 10 requires that nonconformities and incidents feed back into improvement. This is where a risk assessment stops being a document and becomes a management system.
Quantifying cyber risk from theory to practice
The biggest gap in most organisations’ risk assessments is the jump from qualitative labels to numbers that drive decisions. Calling something a high risk does not tell the CFO how much budget to approve.
The Factor Analysis of Information Risk (FAIR) model provides a structured way to calculate risk in monetary terms. Here is a simplified walkthrough.
1
Loss Event Frequency (LEF)
How often do you expect this event to occur? This combines the threat event frequency (how often someone attempts the attack) with the vulnerability rate (the probability that the attempt succeeds given your current controls).
2
Loss Magnitude (LM)
If the event occurs, what is the total cost? This includes primary losses (response costs, replacement costs, lost productivity) and secondary losses (regulatory fines, litigation, customer churn, reputational damage).
3
Risk = LEF × LM
A worked example
1
Threat Event Frequency
Based on industry data and your threat intelligence, you estimate 12 significant attempts per year targeting this system.
2
Vulnerability Rate
Given your current controls (network segmentation, encryption, access controls), you estimate a 5% chance that any given attempt succeeds. That gives you a Loss Event Frequency of 0.6 events per year.
Suppose you are assessing the risk of a data breach affecting your customer database containing 500k records.
3
Primary Loss Magnitude
Incident response, forensics, notification costs, and system restoration come to £640k.
4
Secondary Loss Magnitude
Regulatory fines under GDPR, legal fees, customer churn, and brand damage total £1.76k.
5
Total Loss Magnitude
£2.4m per event.
6
Annualised Loss Exposure (ALE)
0.6 × £2.4m = £1.33m per year.
Now you have a number. If a set of controls costing £320k annually reduces your vulnerability rate from 5% to 1%, your new ALE drops to £288k. The net benefit of that investment is £832k per year. That is the kind of analysis that makes security budgets defensible.
The numbers will not be precise, and they do not need to be. They do need to be reasonable and defensible, however.
Your actionable cybersecurity risk assessment checklist
We have distilled the process above into a downloadable checklist template you can adapt to your organisation’s specific context. It is designed as a starting point rather than a finished product, because every organisation’s risk profile is different. Therefore, the checklist should be customised to reflect your industry, regulatory environment, and technology stack.
The template covers the following domains:
1
Network Security
Firewall configurations, network segmentation, intrusion detection/prevention, wireless security, DNS security.
2
Endpoint Security
Device management, antivirus/EDR deployment, patch management schedule, mobile device policies.
3
Cloud Security
Configuration management, identity and access management for cloud resources, data residency, shared responsibility model documentation.
4
Data Security and Privacy
Data classification, encryption standards, data retention and disposal, backup and recovery testing.
5
Access Management
Least-privilege enforcement, multi-factor authentication coverage, privileged access management, regular access reviews.
6
Incident Response
Plan existence and currency, defined roles and communication protocols, tabletop exercise frequency, post-incident review process.
7
Vendor security assessment process, contractual security requirements, fourth-party risk visibility, SLA monitoring.
8
Employee Awareness
Security training frequency and quality, phishing simulation results, policy acknowledgment tracking.
Each item in the checklist includes a field for current status, risk rating, responsible owner, and remediation deadline. The goal is to turn the assessment into a living document that feeds directly into your risk register and project planning.
Skip the blank page.
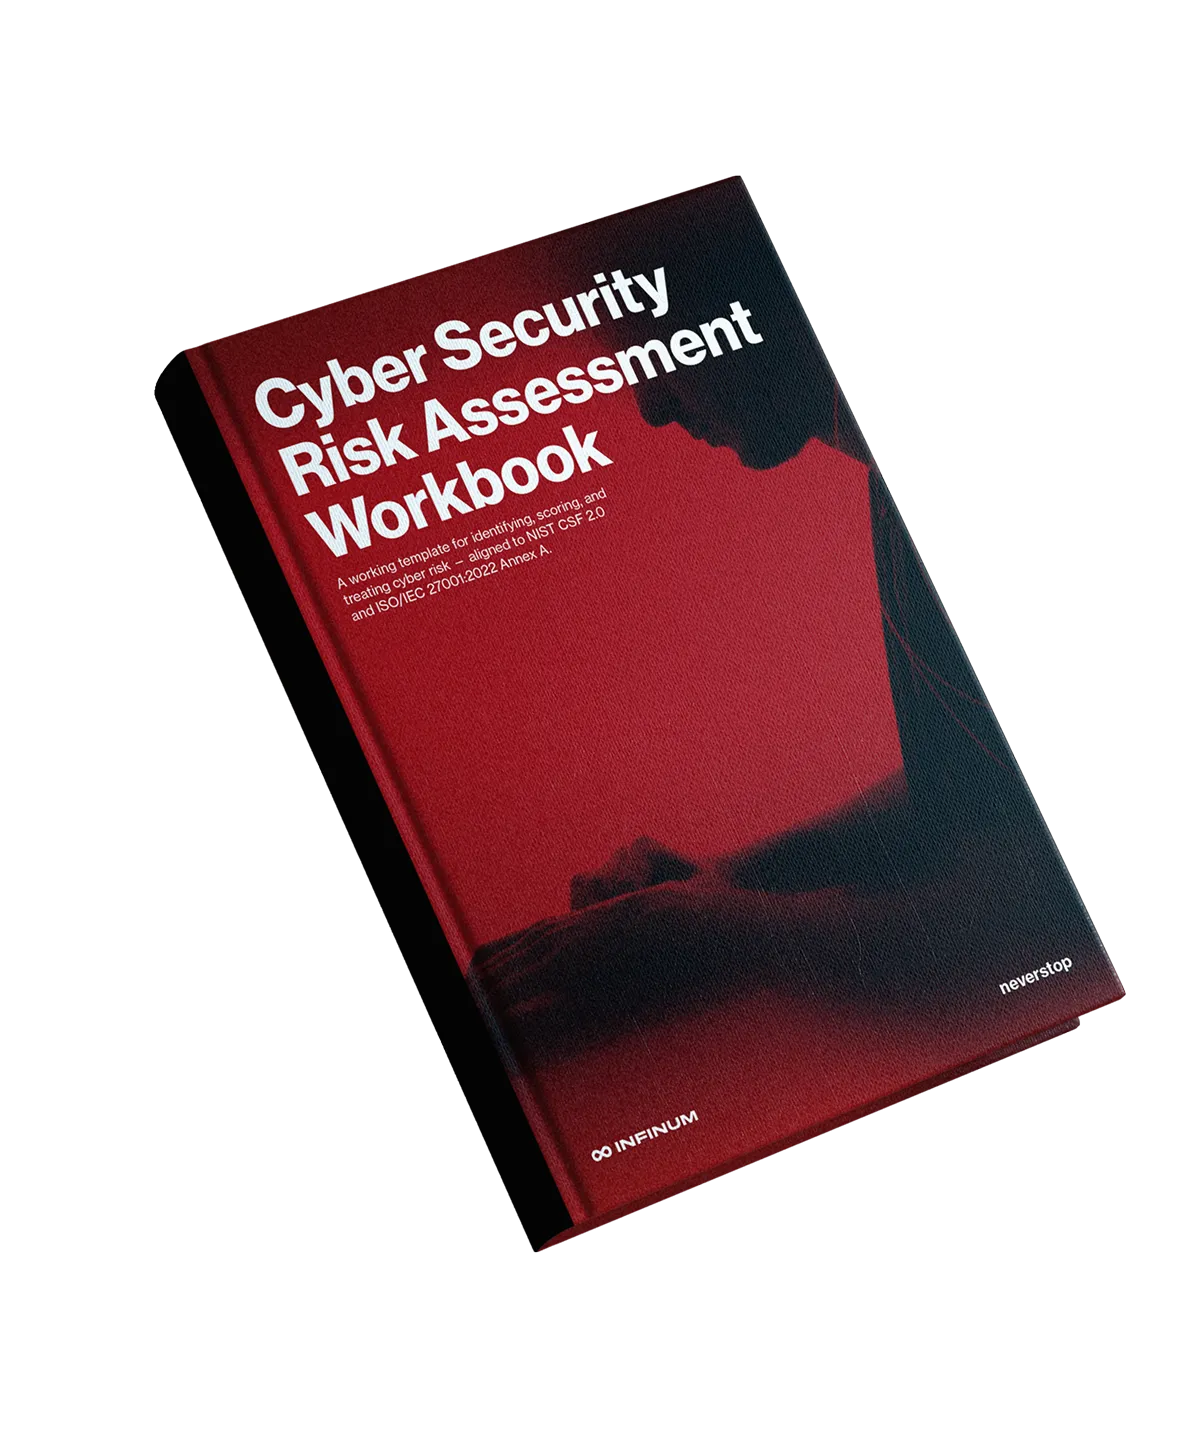
Our free Cyber Security Risk Assessment Workbook has all seven phases built in — scored risk register, heatmap, 93 Annex A controls mapped to NIST CSF 2.0, and an action tracker.
Choosing the right framework
Several security frameworks are available, and the right choice depends on what you are trying to achieve.
1
ISO/IEC 27001
Core philosophy: A certifiable management system standard. Clauses 4 to 10 set out the mandatory requirements for establishing, operating and improving an information security management system (ISMS); Annex A provides a reference set of 93 controls, grouped into organisational, people, physical and technological themes, from which you select based on your risk assessment.
Best for: Organisations that need to demonstrate security maturity to customers, insurers or regulators — particularly B2B and SaaS businesses where an ISO certificate shortens enterprise procurement cycles. It is also the practical baseline for organisations operating across multiple jurisdictions, since it is recognised internationally rather than tied to one regulator.
Strengths: Independently auditable, so the outcome is a certificate a third party will accept rather than a self-assessment. Risk-driven rather than prescriptive, so controls are proportionate to your actual exposure. Annex A maps cleanly onto other frameworks, which means the work supports NIS2, DORA and customer security questionnaires without starting again. The 2022 revision modernised the control set, adding threat intelligence, cloud services, secure coding and data leakage prevention.
Weaknesses: Certification carries real cost and time — typically several months of preparation plus audit fees, and an ongoing surveillance cycle. The standard tells you what must be in place, not how to do it, so implementation guidance has to come from ISO 27002 or elsewhere. It can also become a documentation exercise: a certificate demonstrates that a management system exists and is followed, not that you would withstand a determined attacker.
A note on the difference: ISO 27001 is the standard you certify against. ISO/IEC 27005 is guidance on how to run the risk management process that ISO 27001 requires. They are not alternatives — if you are pursuing ISO 27001, 27005 is the companion that tells you how to do clause 6.1 well.
2
NIST Cybersecurity Framework (CSF)
Core philosophy: Organise cybersecurity activities into five functions (Identify, Protect, Detect, Respond, Recover) with maturity tiers.
Best for: Organisations seeking a broad, flexible framework, especially those in U.S.-regulated industries or working with U.S. federal agencies, and UK and EU defence and government sectors.
Strengths: Widely adopted, vendor-neutral, strong community support, integrates well with other NIST publications (800-53, 800-30).
Weaknesses: More of an organisational framework than a risk assessment methodology, and it does not prescribe how to calculate risk (for this, you would need to use NIST RMF or NIST 800-30).
3
ISO/IEC 27005
Core philosophy: A risk management process aligned with the ISO 27001 information security management system.
Best for: Organisations pursuing ISO 27001 certification or operating in international markets where ISO standards carry weight.
Strengths: Internationally recognised, process-oriented, integrates tightly with ISO 27001 controls.
Weaknesses: Can be bureaucratically heavy, requires significant documentation overhead, and provides less practical guidance on quantification.
| Criteria | NIST CSF | ISO 27005 | ISO 27001 |
| Risk Quantification | Low | Low | Low |
| Implementation Effort | Medium | High | High |
| International Recognition | Medium | High | High (Annex A maps to NIST CSF, NIS2, DORA, SOC 2) |
| Integration with Standards | High (NIST system) | High (ISO 27001) | Yes |
| Independently certifiable | No | No | Yes |
| Best For | Program maturity | Certification | Proving security to customers and regulators |
Tools for an effective cyber risk assessment
Technology will not replace human judgment, but the right tools save hundreds of hours and reduce errors.
Vulnerability Scanners
Scanners like Nessus, Qualys, and OpenVAS automate the discovery of known vulnerabilities across your infrastructure. They provide severity scores that inform your likelihood analysis. But run them regularly rather than only during assessment season.
GRC (Governance, Risk, and Compliance)
Platforms like Archer, ServiceNow GRC, or LogicGate centralise your risk register, automate workflow for risk treatment plans, and generate audit-ready reports. They are worth the investment once your risk program outgrows spreadsheets.
Specialised Risk Quantification Tools
Tools built on the FAIR model (such as RiskLens) help you run Monte Carlo simulations on your loss scenarios, producing probability distributions rather than single-point estimates. These are particularly useful for board-level reporting.
Penetration Testing Platforms and Services
These go beyond scanning to simulate real-world attacks. The findings from a well-scoped pentest are among the highest-value inputs to your risk assessment.
The trap is tool sprawl. Pick tools that integrate with each other and with your existing security stack, as, for example, a vulnerability scanner that cannot feed data into your GRC platform creates manual work that degrades the quality of your assessment over time.
The legal and regulatory imperative for security assessments
For many industries, risk assessments are not optional.
1
DORA (Digital Operational Resilience Act)
The EU’s Digital Operational Resilience Act has applied since January 2025 and covers a broad range of financial entities — banks, insurers, investment firms, payment institutions, crypto-asset service providers — along with the critical ICT third-party providers that serve them.
DORA requires in-scope firms to maintain an ICT risk management framework, which must be documented, reviewed at least annually, and reviewed again after any major incident. It also sets requirements for classifying and reporting major ICT-related incidents to regulators within defined deadlines, for digital operational resilience testing, and for managing ICT third-party risk, including maintaining a register of contractual arrangements and ensuring specific provisions appear in supplier contracts. Significant entities face an additional requirement for threat-led penetration testing.
Two features make DORA more demanding than a general security regime. Responsibility sits explicitly with the management body, which cannot delegate accountability. And supervision extends beyond financial firms themselves to designated critical ICT third-party providers, which are overseen directly at EU level — so a technology supplier can find itself in scope through its customers.
2
The Cyber Security and Resilience Bill (UK)
The Cyber Security and Resilience (Network and Information Systems) Bill was introduced to Parliament in November 2025 and is progressing through the House of Lords. It is not yet law, but organisations in scope should be preparing now rather than waiting for Royal Assent.
The Bill would amend the UK’s Network and Information Systems Regulations 2018 and represents the most significant update to UK cyber regulation since they were introduced. Its main effects are to widen scope, bringing managed service providers and data centres into the regime and allowing government to designate critical suppliers whose products or services underpin essential activities; to strengthen incident reporting; and to give regulators broader enforcement powers, including significantly higher penalties. Supervision follows a sector-specific model, with responsibility distributed across a number of existing regulators rather than concentrated in one.
The Bill broadly aligns with the direction of the EU’s NIS2 Directive, but it is a distinctly UK approach rather than a transposition, and the two regimes differ in scope and mechanism. Organisations operating on both sides of the Channel should not assume that compliance with one delivers compliance with the other.
The practical implication for most organisations is supply chain. Even if you are not directly regulated, customers who are will pass their obligations down through contracts, due diligence questionnaires and assurance requirements — which is usually how these regimes first arrive on a supplier’s desk.
3
NIS2
The EU’s NIS2 Directive requires organisations within its scope to take appropriate and proportionate measures to manage cybersecurity risks, including policies for risk analysis and information system security. It also requires them to address areas such as incident handling, business continuity, supply chain security, and vulnerability management.
4
PCI DSS
This mandates an annual risk assessment process.
The financial consequences of non-compliance are concrete. GDPR fines can reach 4% of global annual revenue, while HIPAA penalties max out at $2.13 million per violation category per year. But the litigation costs and customer loss often dwarf the fines themselves.
Meeting these obligations requires more than conducting an assessment once and filing the results away. Organisations need governance processes that turn risk findings into accountable actions, track remediation, and provide evidence that security and compliance requirements are being managed over time.
This is where GRC consulting can add value. A GRC programme can connect risk assessments with policies, controls, compliance requirements, and reporting, giving security leaders a structured way to manage regulatory obligations and make informed decisions about risk.
A documented, regularly updated risk assessment is your primary evidence that you have met your duty of care. If a breach occurs and you can demonstrate that you identified the risk, evaluated it, and either treated it or consciously accepted it with appropriate rationale, your legal position is materially stronger than if you did nothing.
Building resilience through continuous risk management
A risk assessment dated eighteen months ago reflects a threat environment that no longer exists, as new vulnerabilities are disclosed daily, your infrastructure changes with every sprint, and acquisitions bring unknown technical debt. Regulatory requirements also shift over time.
The assessment process should run on a defined schedule (annually at minimum) and trigger automatically when specific events occur, such as a major system deployment, a merger or acquisition, a change in regulatory requirements, or a significant security incident.
At Infinum, we build these triggers into our clients’ operational processes so the assessment stays current without becoming someone’s side project.
Three practices make continuous risk management work in practice:
- Integrate risk assessment into your development lifecycle: Every new feature, integration, and vendor should go through a lightweight risk review before launch.
- Automate what you can: Continuous vulnerability scanning, automated asset discovery, and real-time configuration monitoring reduce the manual effort of maintaining an accurate risk picture. Reserve human analysis for the judgment calls like likelihood estimation, impact modeling, and treatment decisions.
- Report on risk trends: Show the board how your risk posture is changing quarter over quarter. Are you reducing your annualised loss exposure? Are new risks emerging faster than you are treating existing ones? Trend data tells a story that a static risk register cannot.
The organisations that get this right treat risk assessment as an operating discipline, not just a compliance exercise. Security becomes a shared responsibility rather than a department, and investment decisions get made with the same analytical rigor applied to any other business risk.
Put this into practice
Knowing the steps is one thing. Working through them without losing track of 90 controls, a dozen risk owners and everything you decided six months ago is another.
Our Cyber Security Risk Assessment Workbook is the tool we use ourselves. It takes you through all seven phases in order: scope and ownership, asset register, risk register with automatic inherent and residual scoring, a board-ready heatmap, all 93 ISO 27001:2022 Annex A controls mapped to NIST CSF 2.0, and an action plan that tracks what you decided and whether it actually happened.
It’s free, it’s yours to keep, and nothing in it phones home.
Already completed an assessment?
Already completed an assessment and want to know what you missed? Self-assessment captures the risks you know about. It can’t find the ones you haven’t looked for, or tell you whether a control holds up under attack.
With AMR CyberSecurity now part of Infinum, we bring security risk assessment, governance, and compliance expertise together with our wider technology capabilities. Our GRC consulting services help organisations turn regulatory requirements and risk findings into practical policies, controls, and ongoing governance, supporting frameworks including NIS2 and ISO 27001.