

EVENT INFO
Spend a morning in Ljubljana with Mastercard, Wultra and Infinum working out how regulated industries with sensitive data can stop fraud without losing customers.
Every login, payment and onboarding selfie leaves a trail. It moves through apps, vendors, cloud providers and partners, and few companies can still draw the full map of where it ends up, or say who really controls it.
Meanwhile, fraud is sold as a ready-made service, deepfakes can pass onboarding, and new EU rules are changing how customers prove who they are. Inside every company the same negotiation follows: security adds a step to stop the attack, product removes one to keep the customer. You can’t add friction everywhere, and you can’t strip it all out.
Business Breakfast brings together Mastercard, Wultra and AMR – Part of Infinum for a morning of talks and an open panel on that negotiation: how fraud operations work today, how to roll out phishing-resistant authentication without hurting the user experience, and what attackers find in companies that passed their last audit.
Financial services is where the pressure is highest, so that’s where many examples come from, but the lessons apply to anyone who holds customer data.
You’ll leave knowing which security controls are worth what they cost, which questions to ask about where your data goes, and who in your organisation should own those calls. Breakfast starts at 8:30, and the conversation continues after the panel.
| PROGRAM | |
|---|---|
| 8:30 – 9:00 | Breakfast and arrivals |
| 9:00 – 9:30 | The Age of Cybercrime Máté Nemes, Mastercard |
| 9:30 – 10:00 | Rethinking Banking Authentication Ondřej Kupka, Wultra |
| 10:00 – 10:30 | Penetration Testing and Red Teaming – What Fails Martin Walsham & Sean McCarthy, AMR CyberSecurity by Infinum |
| 10:30 – 11:15 | Panel discussion moderated by Željko Plesac, Infinum |
| 11:15 – 12:30 | Networking and breakfast |
Speaker
The Age of Cybercrime
Máté Nemes
Director, Security Solutions, Mastercard
Máté leads Mastercard’s cybersecurity and fraud-prevention solutions. He has held the role since 2017, after joining the company as a business analyst. He played a key role in introducing Strong Customer Authentication (SCA) and in the optimisation work that followed. He speaks regularly at banking and fintech conferences, and his recent work focuses on how organised cybercrime is evolving and how banks can stop fraud earlier in the attack chain.
In this talk, Máté will:
1
Trace how cybercrime moved from clumsy, easy-to-spot attacks to industrialised, AI-powered scams anyone can buy as a service
2
Share Mastercard research showing that people’s confidence is growing faster than their ability to recognise manipulation
3
Explain why SMEs remain a blind spot, and why banks hold the trust capital even though every player sees only part of each scam
4
Show how machine-speed AI defence, intervening at the moment of risk, and sharing signals across sectors can rebuild trust
Rethinking Banking Authentication: Security, Experience and Regulation
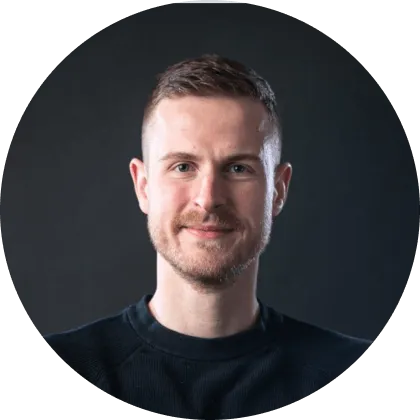
Ondřej Kupka
Regional Lead, Digital Identity, Wultra
Ondřej helps banks and fintechs adopt phishing-resistant authentication and digital identity solutions, and has done so at Wultra since 2022. Wultra is a Prague-based provider of post-quantum authentication technology, used by more than 70 clients in over 25 countries. Before Wultra, he co-founded Nextra Systems. He holds a master’s degree in Cybernetics, Control and Measurement from Brno University of Technology.
In this talk, Ondřej will:
1
Unpack what PSD3/PSR and the EU Digital Identity Wallet mean in practice for identity, authentication and digital transactions
2
Explain the shift towards phishing-resistant authentication
3
Show how banks can strengthen security without adding friction for customers
4
Share what it takes to modernise authentication across devices, channels and customer needs
Penetration Testing and Red Teaming – What Fails
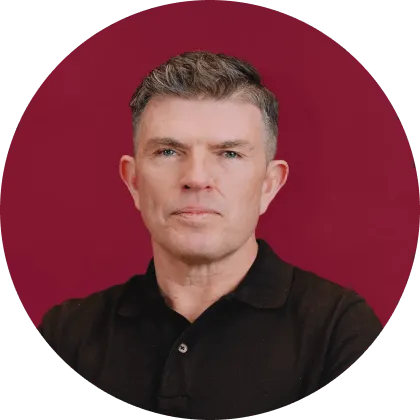
Martin Walsham
Director of Cyber Security, AMR CyberSecurity – Part of Infinum
Martin Walsham, Director of Cyber Security, leads AMR CyberSecurity. He has worked closely with industry, government and regulators on security schemes and standards, and previously sat on the Executive Board of CREST. His expertise spans risk management, security architecture, accreditation and building trusted assurance models for hardware and software.
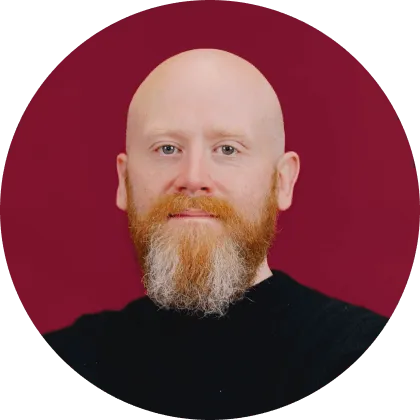
Sean McCarthy
Head of Security Testing Practice, AMR CyberSecurity – Part of Infinum
Sean McCarthy, Head of Security Testing Practice, is a dual-qualified NCSC CHECK and Cyber Scheme Team Leader and an Offensive Security Certified Professional (OSCP). He has delivered technical assurance for government, private and financial-sector clients across the US, France and Germany. He co-created the Department for Transport’s security guidelines for connected autonomous vehicles and has carried out security audits for the Ministry of Defence.
In this talk, Martin and Sean will:
1
Compare penetration testing and red teaming, covering where each adds value and where each stops
2
Set realistic expectations for what security testing can and can’t tell you
3
Walk through recurring real-world issues: exposed credentials, excessive privileges, weak network segregation, and gaps between monitoring and response
4
Show where testing itself fails, from poor scoping to findings that are never fixed or retested
Panel
Fraud, Friction and Identity: Decisions Banks Make in 2026
The panel will tackle the questions banks discuss behind closed doors:
1
How do you stop deep fake onboarding and fraud that scales?
2
Who decides when a security control costs conversion?
3
How much of its security posture can a bank safely outsource?
4
What does the EU wallet mean for banks already running their own identity stack?
Moderator

Željko Plesac
Partnerships Director, Infinum
Željko has spent more than a decade at Infinum, working his way from Android engineer to Technical Director, then Alliance Director, and since 2024, Partnerships Director. He speaks often at conferences and co-organises Android Meetup Slovenia. As moderator, he’ll keep the panel on the decisions banks actually face and leave plenty of room for questions from the audience.


